Security Incident at Gnosis Pay Compromises Customer Card Information and Wallet Data
Despite the breach revealing sensitive personal and financial details, the cryptocurrency debit card company confirmed that customer funds were not compromised.
On Friday, Gnosis Pay, a provider of Visa debit cards linked to cryptocurrency, announced a data breach that resulted in the exposure of customers' debit card information, residential addresses, and digital wallet addresses associated with cryptocurrencies.
The company stated that it identified the unauthorized intrusion into its older consumer card infrastructure on Nov. 3 and initiated containment procedures within a two-hour timeframe. Gnosis Pay emphasized that customer assets remained secure and that its distinct enterprise platform, which facilitates white-label card solutions, experienced no impact from the incident.
Based on breach notification documents examined by Cointelegraph, the organization determined that the compromised information encompassed complete payment card numbers, card expiration dates, security CVV codes, full customer names, residential addresses, and cryptocurrency wallet addresses associated with the impacted accounts. Additional exposed data included email addresses, telephone numbers, nationality information, and in certain instances, banking credentials such as IBAN and BIC codes.
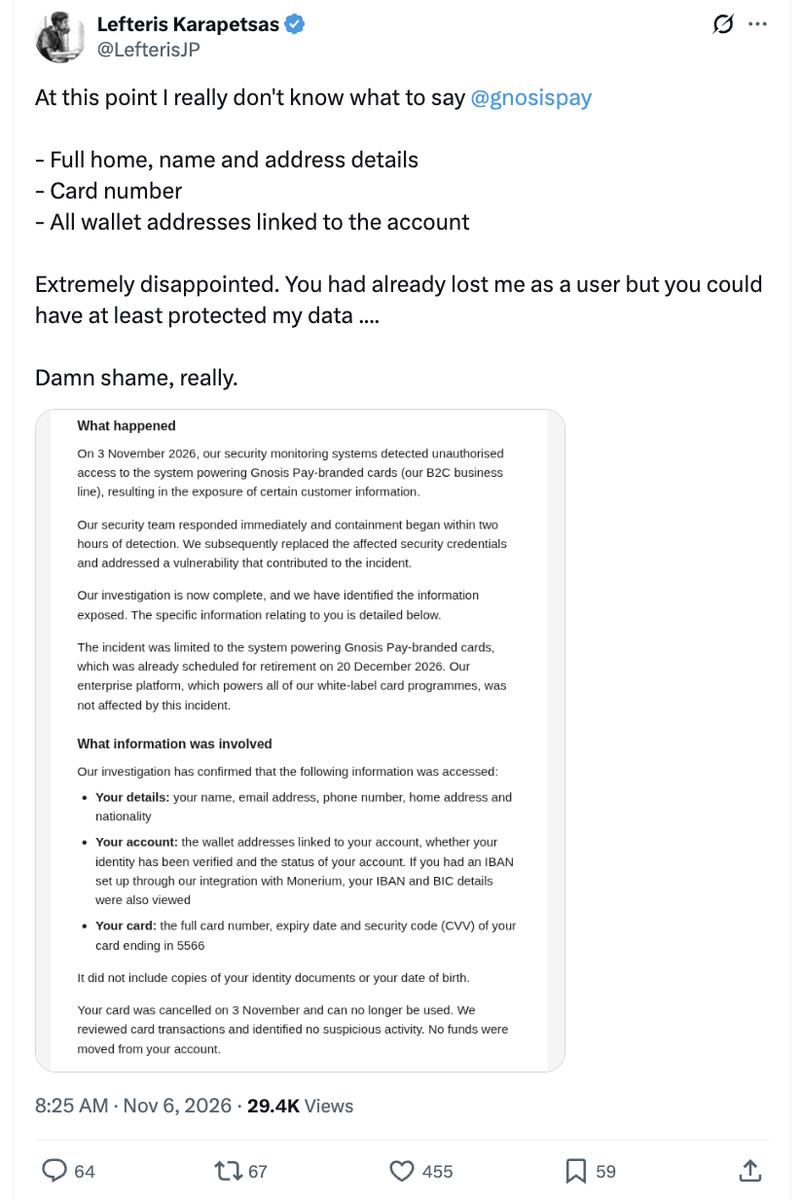
A particular notification additionally verified that the affected customer's card underwent cancellation on Nov. 3, with the company reporting no detection of fraudulent transactions or unauthorized fund transfers.
According to Gnosis Pay's statement, the company has replaced the breached security access credentials, remediated the security weakness, and implemented mandatory 3D Secure authentication for all online transactions pending the legacy system's scheduled decommissioning on Dec. 20. The company also cautioned users to remain vigilant against phishing schemes that might leverage their personal information or transaction history, and indicated it was organizing monitoring services to detect potential misuse of the compromised information.
Information sourced from OpenRate, an independent platform that monitors crypto card usage, indicates that Gnosis Pay maintained approximately 2,400 daily active cardholders and facilitated $263,200 worth of transactions during the preceding 24-hour period.
The organization has not revealed the total number of impacted customers and failed to provide an immediate response to Cointelegraph's inquiry for additional comments.