Cryptocurrency wallet loses $6.45M in suspected security breach involving compromised credentials
Approximately $6.45 million in digital assets was withdrawn from a Safe wallet in what Zodiac's co-founder attributes to compromised credentials combined with excessively broad permission configurations.
Approximately $6.45 million in cryptocurrency was withdrawn from a Safe wallet on Monday, according to reports, with the co-founder of Zodiac attributing the incident to what appears to be a compromised security key combined with excessively permissive wallet configuration settings, rather than any weakness in Zodiac's smart contract infrastructure.
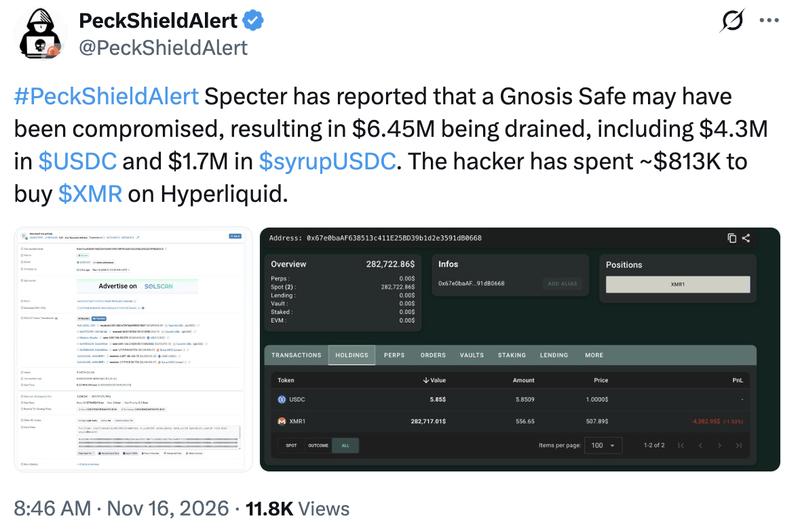
The suspected unauthorized withdrawal was initially flagged by blockchain security company PeckShield, which referenced analysis from onchain investigator Specter. Transaction records on the Ethereum blockchain examined by Cointelegraph reveal that roughly 4.39 million USDC along with 1.72 million syrupUSDC tokens were moved out of the wallet through a single transaction executed on Monday.
In a statement to Cointelegraph, Johannes Moormann, who co-founded Zodiac, explained that his team analyzed the transaction and verified that it successfully passed through the wallet's Zodiac Roles Modifier, a system that validates transfers against the wallet's established permissions policy before allowing them to proceed. "There is no vulnerability in the module. The contracts worked correctly. The transaction came from the key of a long-standing role member, which was most likely compromised," he said.
Moormann further explained that the custom permissions policy configured for the wallet permitted the transaction to go through, though this was almost certainly not the intended outcome. He clarified that the wallet's operators maintained full control over both the security keys and permission settings, and that Zodiac neither had access to these components nor played any role in configuring the wallet's initial setup. The Zodiac team has not established communication with those affected by the incident.
The Zodiac Roles module was initially identified by Specter as a component involved in the suspected unauthorized activity. PeckShield's analysis also revealed that the individual responsible for the withdrawal converted approximately $813,000 of the stolen funds into tokens linked to Monero on the Hyperliquid platform.
The Zodiac Roles module provides Safe wallet users with functionality to designate permissions for particular transaction types. According to Moormann, this incident does not suggest the existence of a security vulnerability that would affect other wallets utilizing the same module.
The individual or entity controlling the affected wallet remains unidentified. Cointelegraph reached out to both Safe and Gnosis Guild requesting comments on the matter but had not received any response prior to the time of publication.
Bitquery flags similar fund flows
Bitquery, a blockchain analytics company, followed the movement of funds originating from the compromised Safe wallet as they flowed through several intermediary addresses before arriving at Hyperliquid, where five separate accounts collectively acquired roughly $1 million worth of XMR1 tokens.
The analytics firm observed patterns resembling the movement of funds that occurred after Monday's incident involving Lighter, which included a transfer of 160 Ether (ETH) as well as acquisitions of XMR1 tokens.
Nevertheless, Bitquery reported that its investigation uncovered no direct transfer connections linking the two separate groups of wallets and therefore cannot definitively determine whether a single entity was responsible for both incidents.