Race Against Time: How Binance Hackers Scrambled to Liquidate Billions in Digital Assets
In a frantic bid to preserve their ill-gotten gains, cybercriminals rushed to exchange stolen stablecoins for non-freezable cryptocurrencies while major issuers including Tether and Circle worked to lock down billions in digital assets.
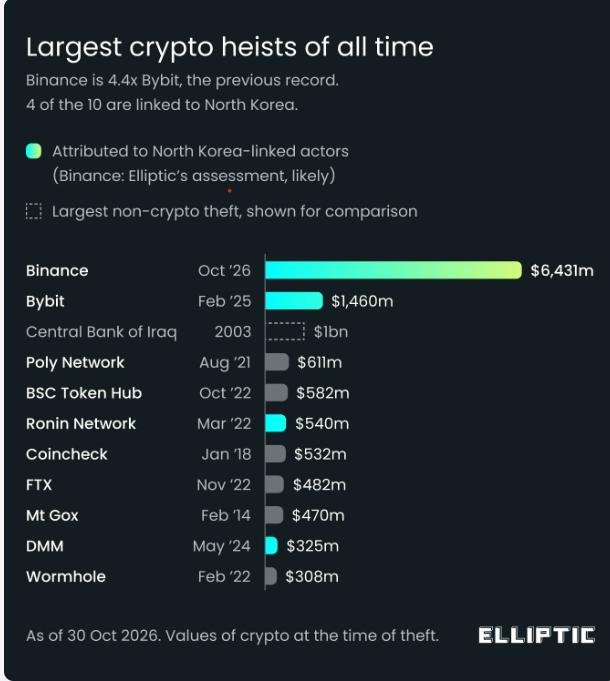
The perpetrators of the massive Binance breach, valued at approximately $6.3 billion, retain control over several billion dollars in pilfered digital currency, even as token issuers have taken aggressive steps to freeze the stolen proceeds.
This unprecedented incident, representing the most significant cryptocurrency heist on record, commenced at 8:04 pm UTC on Thursday, with the culprits—traced to the identical North Korean cybercriminal group responsible for the Bitget breach last month—initiating asset conversions without delay.
The strategic approach employed by the cybercriminals involved transforming freezable assets, including USDT and USDC, into alternative cryptocurrencies that cannot be immobilized, such as Bitcoin (BTC) and Ether (ETH).
Tracking the movement of funds, CertiK engineer Dickson Wu identified $500 million in USDT transferred to a single address, with $325 million exchanged with market makers for ETH by 20:59 UTC, within the first 55 minutes following the breach's commencement.
The hackers found themselves in a desperate race against the cryptocurrency industry's most influential authorities: stablecoin behemoths such as Tether and Circle, both of which had promptly initiated the process of blacklisting wallet addresses connected to the criminal activity.
According to Binance's Friday announcement, approximately $3 billion of the compromised assets had been frozen on the blockchain from the total estimated loss of $6.3 billion, with the exchange collaborating alongside law enforcement agencies, token issuers, and blockchain forensics companies to locate the remaining funds.
The magnitude of this heist is staggering by any standard, particularly within the cryptocurrency sector, yet with roughly half the stolen assets already immobilized, what portion of the pilfered crypto remains accessible to the criminals for actual use?
Crypto with an off switch
In stark contrast to BTC or ETH, which operate as decentralized digital currencies without any central authority capable of implementing controls, centralized stablecoins such as Tether's USDT and Circle's USDC feature issuers with the technical capability to freeze tokens residing at designated wallet addresses.
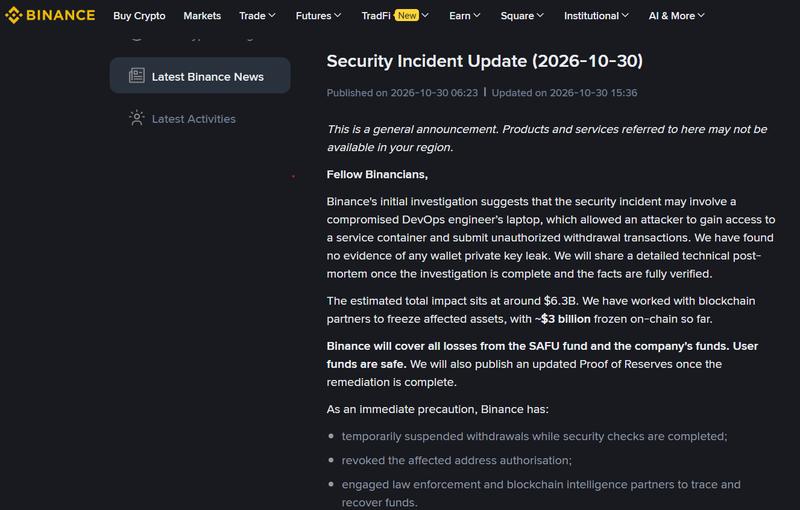
This functionality provides these entities with the authority to respond rapidly when situations like this arise. Tether executed a freeze on approximately $1.567 billion in USDT across all affected addresses, with the initial substantial freeze occurring merely 37 minutes following the arrival of stolen assets in the attacker's primary Ethereum wallet.
Circle implemented a freeze affecting roughly $823 million in USDC just three minutes thereafter, followed shortly by additional issuers including Ripple and World Liberty Financial implementing similar measures.
The capacity to freeze cryptocurrency assets isn't limited solely to stablecoins, and even without centralized governance, certain decentralized protocols such as Arbitrum took proactive measures in response.
The Security Council of Arbitrum transferred approximately $30.5 million in ARB and ETH into an intermediate frozen wallet, establishing conditions whereby these funds can only be relocated following additional Security Council intervention or through a governance vote conducted by the Arbitrum DAO.
A critical distinction must be acknowledged—the freezing of funds does not automatically translate to their recovery. While immobilizing these assets successfully prevents the suspected perpetrators from utilizing them, this action doesn't inherently result in their return to Binance or the affected users.
The Aave complication
The decentralized lending platform Aave introduces an additional dimension of complexity to this situation. During the timeframe between 20:58 and 21:01 UTC, a wallet linked to the attackers placed $60 million in USDT into Aave V3 on the Ethereum network and secured a loan of $44.6 million in wrapped Ether (WETH), approximately 40 minutes prior to the implementation of the first freeze.
In its 1:00 am status update, LlamaRisk, serving as an Aave risk service provider, reported that the position held by the attacker subsequently contained roughly $59.9 million in USDT collateral backing $43.8 million in outstanding debt. Aave confirmed the position maintained overcollateralization status and posed no threat to protocol suppliers.
Given that the USDT had already entered Aave's lending pool prior to blacklisting measures, simply blacklisting the attacker's wallet address could not automatically retrieve the collateral now held within the protocol's custody, as Marc Zeller, founder of Aave Chan Initiative, clarified:
USDT is real money backed by dollars, and the position is criminal but overcollateralized in the eyes of the protocol.
As a preventative measure against additional deposits and borrowing activity, Aave implemented a temporary freeze affecting markets throughout its V3 and V4 deployments, though existing users maintained their ability to withdraw their funds, settle outstanding loans, and execute liquidation of positions.
Aave subsequently removed its precautionary freeze from V3 and V4 markets, confirming that its smart contracts remained uncompromised and all positions continued to maintain overcollateralization status.
"Just another day in crypto," Zeller remarked.
So what can the attackers actually keep?
Based on Elliptic's calculations, $2.84 billion had been successfully frozen by 7:00 am UTC Friday morning, while the perpetrators maintained control over approximately $3.33 billion in assets that issuers lacked the technical capability to immobilize.
Despite the freeze cutting the attackers' potential gains nearly in half, this development doesn't guarantee the safety or eventual recovery of all the remaining funds.
Bitcoin and Ether operate without centralized token issuers possessing the authority to blacklist specific addresses in the manner available to Tether or Circle. Consequently, once stolen assets undergo conversion into these native cryptocurrencies, while transactions may face certain restrictions, implementing freezes becomes significantly more challenging.
Binance has made a commitment to compensate all losses through its Secure Asset Fund for Users (SAFU) combined with company funds, maintaining that user assets continue to remain secure; per the most recent communication from Binance chief executive Richard Teng, the exchange has already begun "recovering stolen assets for users."