AI-Powered Hacking Tools Automatically Discover and Exploit Vulnerabilities, Google Reports
Cybercriminals are deploying artificial intelligence agents that autonomously identify and exploit software vulnerabilities, narrowing the window for companies to implement security patches, according to Google.
According to the Google Threat Intelligence Group (GTIG), researchers have documented the first instances of cybercriminals deploying AI large language model (LLM) frameworks that autonomously discover and exploit software vulnerabilities without requiring human guidance at each step.
Researchers detailed their findings in a report released on Monday, outlining the discovery of an automated tool on an accessible staging server. This tool performed version comparisons of software, pinpointed potential security weaknesses, and both created and ran exploit code.
"In the past quarter, GTIG identified threat actors using LLM frameworks to fully automate vulnerability discovery and exploitation without a human in the loop for the first time," the researchers said.
The intelligence group discovered an accessible staging server that housed a multi-agent framework designed for vulnerability research and weaponization. This system was configured to perform ongoing differential analysis, examining code changes before and after patch releases for widely-used web applications. The AI model operated independently to identify and take advantage of software security flaws.
The tech giant cautioned that such automated processes are compressing the timeframe available for organizations to deploy security patches before malicious actors create methods to exploit systems with vulnerabilities.
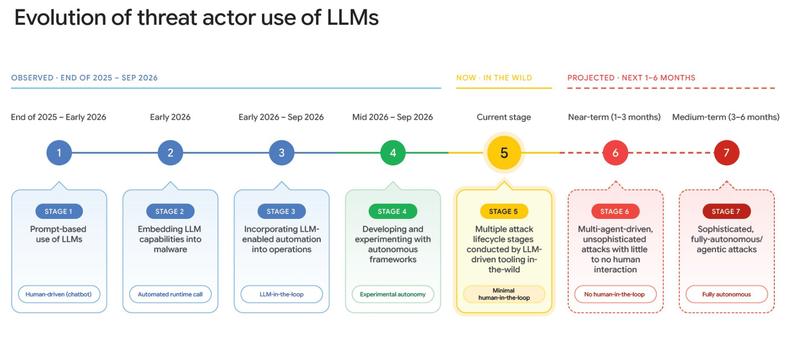
In its September report, GTIG said it had "not yet observed threat actors deploying fully autonomous pipelines against targets in the wild."
AI agents shorten patching windows
Malicious actors are utilizing AI agent frameworks to automate the reverse engineering of patches through differential analysis and are weaponizing N-day vulnerabilities, which are publicly disclosed security flaws.
According to the report, LLMs are empowering cybercriminals to expand "exploitation pipelines against internet-facing servers without human intervention."
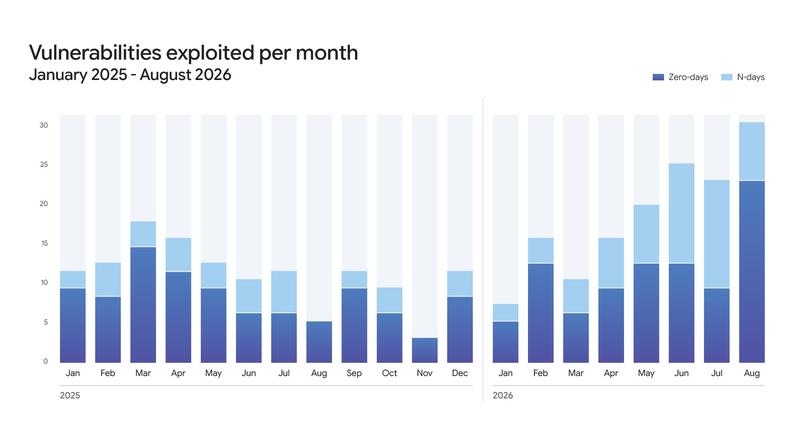
Based on Google's data, vulnerability disclosures more than doubled during the period from January to August. The monthly average of exploited zero-day vulnerabilities was eight in 2025 and climbed to 11 per month between January and August 2026, with August alone seeing 22 such exploits.
Such automated workflows are also speeding up the ability of attackers to progress from gaining initial access to achieving domain administrator privileges. The report referenced an August 2026 campaign targeting PaperCut where attackers obtained that degree of control in a matter of minutes, based on findings from cybersecurity company GreyNoise.
In October, Cloudflare additionally documented exploitation attempts targeting PHP flaws against its client base. According to GTIG, the two PHP vulnerabilities targeted in these exploitation efforts were identified through LLM analysis, as technical details made available prior to the Oct. 21 patch allowed both security researchers and attackers to analyze vulnerabilities and develop exploits, the report stated.
In a September report, AI company Anthropic also warned that AI-assisted attacks have evolved into multi-agent operations automating most of the cyberattack cycle from discovery to exploitation and data theft.
Anthropic described threat actors running "multi-victim campaigns using agentic AI that would previously have required teams of operators."