Revolut reports zero direct communication following public $3M ransom threat
Following an initial demand for 10,000 Bitcoin, a $3 million Monero ransom threat aimed at Revolut has emerged as competing online actors claim to be behind the customer data breach.
On Thursday, Revolut confirmed that despite facing several public ransom demands, it has not been directly contacted by any parties claiming to have executed a breach of customer data.
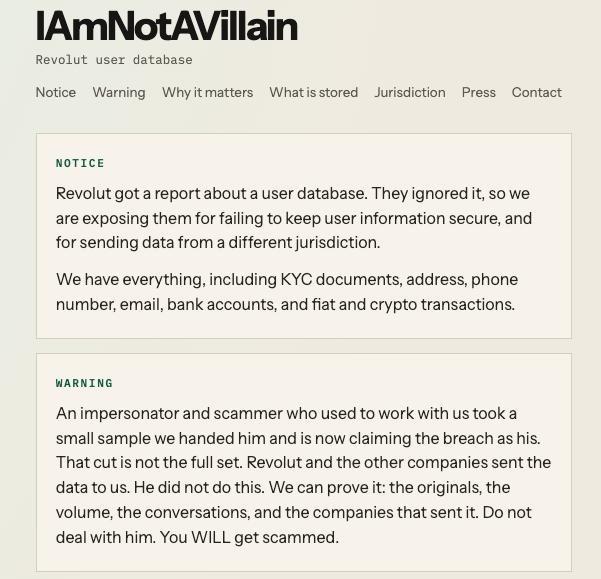
According to a Wednesday Financial Times report, an entity identifying as "IAmNotAVillain" issued a public demand for 6,000 Monero (XMR), approximately $3 million in value, giving Revolut a 24-hour deadline and warning that customer records would be sold to additional criminal organizations if the ransom went unpaid.
"Revolut has not received any direct contact or demand from the individuals or group making these claims," a Revolut spokesperson told Cointelegraph.
This public threat represents the most recent chapter in a data breach that Revolut initially made public last week, while Italian law enforcement agencies have now expanded their probe into allegations that a government email account was exploited to access customer information.
One breach, multiple ransom demands
The assertion by Revolut that no direct communication has occurred heightens confusion surrounding the identity of those behind the public extortion attempt, particularly since "IAmNotAVillain" isn't the sole entity claiming credit for the security incident. When Cointelegraph attempted to access its website, iamnotavillain.xyz, at the time of publication, the site was not available.
A previous entity identifying itself as "Revolut Smilik" had allegedly demanded 10,000 Bitcoin, valued at approximately $780 million at that time, representing a significantly larger sum than the current $3 million Monero demand from IAmNotAVillain.
Through a statement posted on its website, IAmNotAVillain challenged the competing claim, asserting that a previous collaborator had obtained merely a limited sample of the data before claiming responsibility for the entire breach. The site cautioned others against engaging with the competing claimant.
Additionally, Dark Web Informer, an account focused on cybersecurity matters, drew attention to yet another website, revoloot.lol, linked to a different individual claiming responsibility, adding further complexity to determining who actually possesses the compromised customer records. When Cointelegraph checked, the revoloot.lol website was similarly unavailable.
Italian authorities widen Revolut data breach probe
According to a Wednesday report from Italian news agency ANSA, Italy's National Anti-Mafia and Anti-Terrorism Directorate has now joined the investigation due to the suspected intrusion involving a government entity.
An investigation into unauthorized access to a computer system of public interest has been launched by prosecutors in Reggio Calabria, with investigators currently working to determine whether the institutional email account was compromised through a breach or through cloning.
Separately, Italy's privacy regulator has requested that banks conduct urgent security reviews of their access systems and is currently examining whether additional banks or financial institutions may have been compromised.