XMR1 Token Plummets 99.8% Following Alleged $13.5M Security Breach
Blockchain analytics platform Bitquery identified $13.5 million in questionable wrapped Monero token transactions, while the service operator cited a security compromise and vowed reimbursement for impacted users.
On Friday, a wrapped variant of Monero (XMR) experienced a catastrophic decline exceeding 99% on the Hyperliquid platform following suspicious activity from a wallet that obtained tokens directly from the deployer address, moving roughly $13.5 million worth of the digital asset, based on data from blockchain intelligence company Bitquery.
The digital asset, identified as XMR1, collapsed from approximately $500 down to $1 within a time span of about 30 minutes, representing a 99.8% price drop, as documented by Bitquery. These wrapped tokens serve as representations of other digital currencies on alternative blockchain networks, enabling cross-platform trading beyond their original ecosystems. The dramatic collapse impacted XMR1 specifically and not the original Monero cryptocurrency.
Based on Bitquery's blockchain analysis, the implicated wallet obtained 5.2 million XMR1 tokens directly from the deployer address prior to liquidating approximately $13.5 million of the tokens on Friday.
The analytics company tracked $13.28 million in USDC that was moved to Arbitrum, where $13.22 million underwent conversion into 7,467 Ether (ETH) via CoW Protocol. The majority of the acquired ETH was then transferred across a bridge to the Ethereum network.
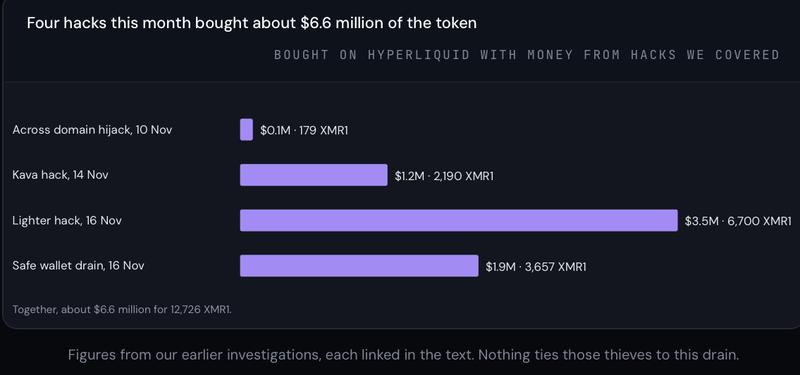
Bitquery's investigation also revealed that stolen funds from four separate security incidents that occurred earlier in November, specifically targeting Across Protocol, Kava, Lighter and Safe, had been utilized to acquire roughly $6.6 million in XMR1 tokens, seemingly as a pathway to convert into native Monero. The analytics firm indicated it discovered no blockchain evidence connecting these previous incidents to the suspected exploit that occurred on Friday.
According to Bitquery, their blockchain examination was unable to determine the method by which the deployer account's private key was accessed or identify who maintained control over it throughout the token transfers, leaving the specific details of the alleged security compromise without confirmation.
Wagyu operator blames suspected infrastructure breach
The pseudonymous individual known as PerpetualCow, who operates Wagyu, the platform responsible for XMR1, ascribed the token's collapse to a purported security breach at hosting company 1984, asserting that client information and confidential server documentation had been compromised.
As explained by PerpetualCow, the private key for the XMR1 deployer had been housed on a server that was later erased, however the hosting company purportedly maintained logs and documentation connected to that server.
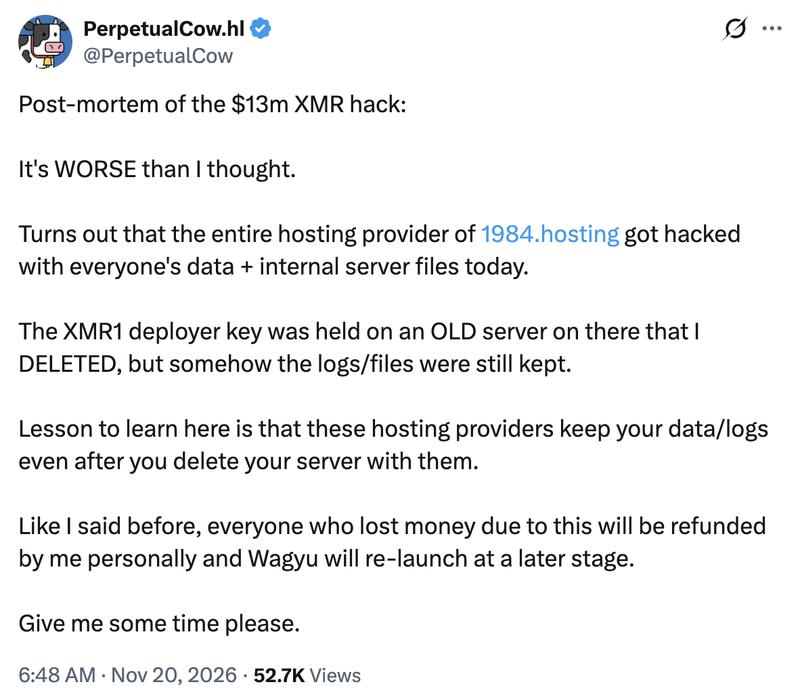
PerpetualCow additionally committed to covering reimbursements for impacted traders from personal funds and indicated that Wagyu would resume operations at an undetermined future date, though no specific schedule was disclosed.
Cointelegraph reached out to the operator seeking further information regarding the purported security breach and compensation strategy but did not receive a reply before this article's publication.