New Ethereum DeFi Protection System Sparks Debate About Transaction Censorship
Designed to shield DeFi platforms from exploits and hacking attempts through pre-settlement transaction filtering, Phylax's security solution has drawn criticism over potential censorship implications and the consolidation of power among Ethereum builders.
A newly launched security infrastructure from Phylax offers decentralized finance (DeFi) platforms a mechanism to intercept and block suspicious transactions prior to settlement on the blockchain.
The innovation could strengthen cryptocurrency defenses against threat actors including North Korean hackers and entities subject to United States sanctions, though it simultaneously creates a pathway to disable smart contract functionality without explicitly granting anyone such authority.
This type of control mechanism has sparked concerns that the technology might evolve into a centralized enforcement tool for authorities rather than serving the principles of decentralized finance.
The question is not just whether there is risk, but if it's acceptable risk.
Stefanie Boss, co-author of research on censorship resistance and compliance behavior in Ethereum's consensus mechanism
"In this case, I'd lean toward that it is acceptable, as the goal is to make the network safer and more aligned with the network and application values," she says.
A security mechanism with a potential freeze risk
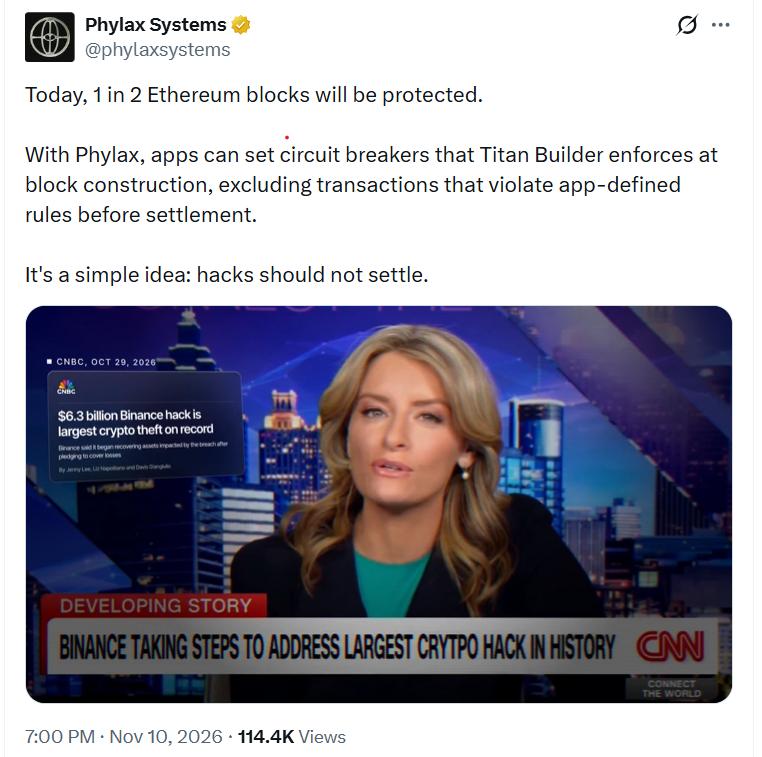
Revealed on Nov. 10, Phylax's partnership with block builder Titan Builder enables Ethereum-based applications to establish criteria that filter out transactions potentially leading to detrimental results during the block construction phase.
Titan, which according to Phylax constructs one out of every two blocks on Ethereum, validates transactions against these predetermined criteria before incorporating them into blocks.
The objective is to block exploits from reaching finality rather than depending on surveillance systems or emergency responses after an attack has already commenced. "Our mission: stop users from losing money to hacks and errors in DeFi," the announcement said.
In a blog Phylax uses the scenario of a vulnerable vault that could mistakenly release $1 million to a user whose shares are only worth $1,000. With the system in operation, a circuit breaker could cap the amount leaving the vault in a single transaction, preventing the funds from being drained.
Comparable protective measures could also theoretically minimize losses in significant breaches like the $6.3 billion Binance hack or the $380 million Bitget exploit, where malicious actors drained exchange wallets and were able to move large amounts of crypto through decentralized protocols.
Although stopping malicious transactions would benefit the cryptocurrency ecosystem, Gabriel Shapiro, a lawyer specializing in digital assets, cautioned that applications utilizing the system could become practically freezable should builders discontinue providing the necessary attestations.
His explanation detailed how smart contracts can be programmed to refuse transactions unless they're incorporated in blocks from builders that have executed the requisite security validations. Should those builders cease providing attestations, protected functions could continuously reject transactions until service restoration.
Odysseas Lamtzidis, founder and chief executive of Phylax, indicates that protocols can circumvent that risk by permitting transactions to proceed even during periods when the system's security validations are inaccessible.
"The sane default we provide and suggest to protocols is a fail-open behavior," he tells Magazine.
However, this protective measure remains optional, placing the decision-making authority with individual protocols regarding how much emphasis to place on security versus availability. "Some protocols might choose to prioritize safety over liveness," Lamtzidis says.
He also says protocols can decide whether their smart contracts are immutable or can be changed through governance.
Shapiro's position is that fail-open protections should be mandated and modifications to the safeguards should be subjected to time-delay mechanisms to prevent protocols from eliminating them instantly.
Ethereum's builder concentration problem
An additional broader worry exists regarding whether the system might strengthen Ethereum's already significantly concentrated market for block building.
Fan Zhang, an Ethereum researcher, contends that Phylax's technology is only achieving practical viability at this juncture due to that concentration. "We finally have a way to implement this effectively," he says, "but sadly only because of how centralized Ethereum's builder market has become."
Zhang says Phylax's approach has "appealing security benefits, especially in the age of AI bots being able to find bugs faster than ever."
Yet he cautions that introducing supplementary code at such a vital juncture in transaction processing generates new failure modes, including implementation errors and builder signing-key theft, loss or impersonation.
"I think the community is very concerned about centralized builders and is making efforts to address them. So I'm concerned that these efforts may undermine each other," he adds.
Sen Yang, an Ethereum researcher, tells Magazine, "If major protocols rely on a small number of builders for security enforcement, this could give those builders a competitive advantage and further exacerbate market concentration."
His assessment suggests that Ethereum's proposed enshrined proposer-builder separation (ePBS) upgrade, scheduled for inclusion in the upcoming Glamsterdam upgrade, may reduce reliance on third-party relays, "but it does not directly address builder market concentration."
According to Yang, transactions excluded by dominant builders could still be included by non-censoring builders, potentially causing delays rather than permanent exclusion.
Where does security become censorship?
Phylax maintains that its system doesn't introduce novel authority over Ethereum transactions since applications themselves establish the rules. The technology is "explicitly opt-in," Lamtzidis says.
He draws parallels between the checks and conditions already embedded within smart contracts. "It's no different than a 'require()' statement," he says. "Censorship implies arbitrary decision-making or coercion."
Zhang draws a similar distinction between applications voluntarily filtering transactions and external parties imposing censorship. "Applications willingly signing up for filtering is fine, as a user can walk away from such applications," he says. "It's externally forced censorship that's the problem. That's where I'll draw the line."
Boss indicates that rules targeting a transaction's outcome are less concerning than those targeting who is making it. "In this case, it is also result-driven, which is often considered less risky," she says.
She views the security objective as legitimate, maintaining that "the harm of those hacks is much higher than the harm of this type of exclusion."
Nevertheless, she cautions that rules could also be deployed to enforce sanctions or politically motivated exclusions.
"It is important to ensure that there are proper safeguards in place to make sure that these rules will remain fair and designed for security," she says.