Crypto Exchanges Pull SignalPlus API Access Following Microsoft Teams Phishing Compromise
Following a security incident, SignalPlus reported that hackers infiltrated an employee's workstation, causing damages under $82,000. The cryptocurrency trading service has committed to fully compensating all affected customers.
Major cryptocurrency exchanges Binance and Deribit announced Thursday that they had disabled API keys associated with SignalPlus, a crypto derivatives trading platform, as a protective measure after a security incident. The exchanges confirmed their internal infrastructure remained secure and uncompromised, though Deribit cautioned that its users would experience interruptions to trading, monitoring, and automated functions performed through SignalPlus.
Yi He, co-founder of Binance, additionally called on all third-party platforms that maintain integrations with the exchange to conduct thorough security audits and watch for anomalous activity, emphasizing that the security risk was not isolated to a single organization.
The platform SignalPlus delivers trading infrastructure specifically designed for crypto derivatives markets, with a focus on options trading, enabling professional traders and institutional clients to oversee positions across various exchanges from a unified interface.
Based on SignalPlus's statement posted on X, the security breach stemmed from a hijacked Telegram account that belonged to an associate at an external technology partner. The malicious actor assumed the identity of this contact and transmitted a fraudulent Microsoft Teams meeting link to one of SignalPlus's engineers, successfully infiltrating the employee's workstation.
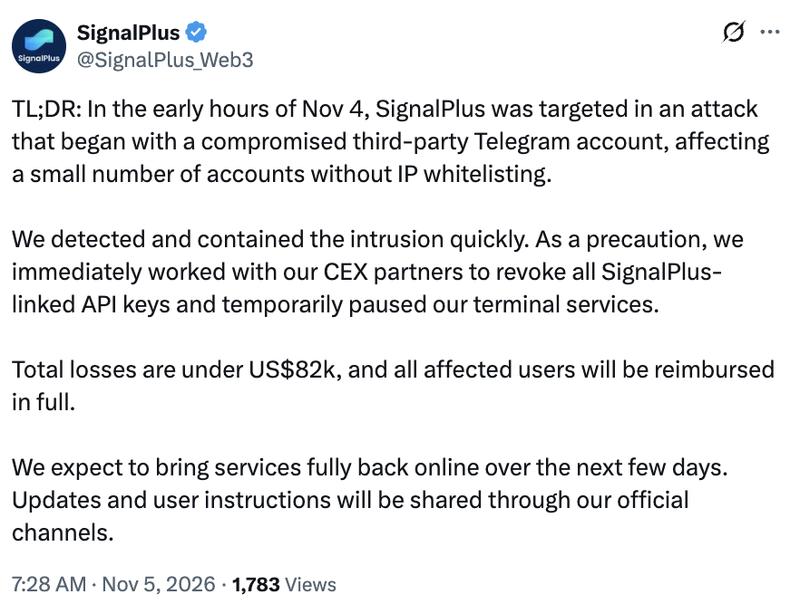
According to the company's disclosure, the malicious actor stayed inactive on the infected workstation for a period before exploiting the engineer's system permissions to penetrate SignalPlus's internal infrastructure during the early hours of Wednesday.
The company reported that it successfully identified and isolated the security breach, with cumulative financial damages totaling less than $82,000, and had initiated the process of providing complete reimbursements to all impacted customers. SignalPlus has placed its services on temporary hold and anticipates resuming full operations within the coming days following the completion of comprehensive security assessments and the implementation of necessary patches.
The platform also admitted that it had failed to implement IP whitelisting protocols for exchange API connections. "We take responsibility for this oversight," the company stated, while announcing plans to implement more stringent API access controls and reinforce its internal cybersecurity measures. IP whitelisting functions as a protective mechanism that limits API connectivity exclusively to a predetermined set of authorized internet protocol addresses.
SignalPlus attack follows $6.3B Binance hack
The security compromise at SignalPlus occurred just days following Binance's revelation of specifics regarding a massive $6.3 billion cyberattack that took place on Oct. 29, which similarly involved the infiltration of staff members' computers.
As outlined in Binance's incident analysis, cybercriminals masquerading as job recruiters deceived an engineer into executing a harmful file presented as a programming challenge. The perpetrators then leveraged the infected workstation to penetrate supplementary systems and ultimately compromised the exchange's digital wallet infrastructure.
On Tuesday, Binance co-founder Yi He revealed that the exchange had identified and thwarted 57 suspected cyberattack attempts linked to North Korea throughout 2026, encompassing fake employment interviews, corrupted software repositories, and efforts to obtain employee login credentials.