Bitget Chief Executive Expresses Doubts About Full Recovery of $388M Stolen Crypto
According to Gracy Chen, the 2025 Bybit security incident serves as a "good reference point" for Bitget's own breach, highlighting that only a minimal portion of stolen funds were successfully frozen or retrieved.
Bitget's chief executive officer has expressed uncertainty about the cryptocurrency exchange's ability to completely freeze or retrieve all digital assets that were compromised during last week's security incident, which led to the disappearance of $388 million in cryptocurrency.
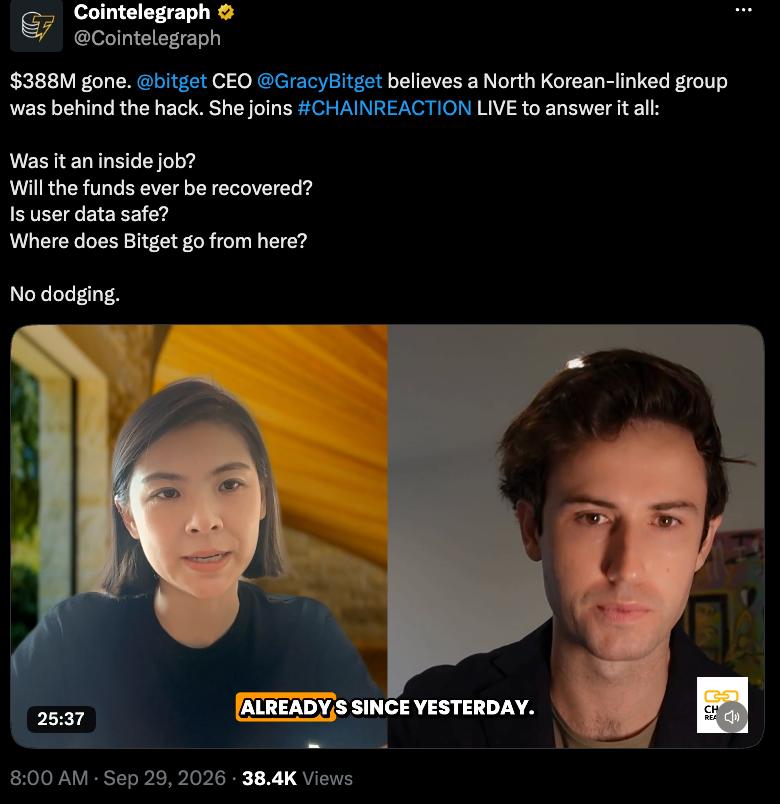
During an appearance on Cointelegraph's Chain Reaction podcast published on Tuesday, Gracy Chen, who serves as Bitget's CEO, indicated that she was using the crypto exchange Bybit's February 2025 security breach as a "good reference point" when analyzing Thursday's attack. During that incident, malicious actors managed to steal approximately $1.5 billion worth of Ether (ETH) from Bybit, with the exchange managing to freeze and recover only a combined total of $80 million.
"I'm actually not very optimistic because after a year or so of Bybit's hack, they've only [been able to freeze] about 3.5% of the total stolen funds," said Chen. "That's only the freezing. It's not about recovery yet."
In the wake of the security incident, Bitget initiated a bounty program that provides 5% of funds that are frozen and an additional 5% for those that are recovered. A number of entities have already taken steps to help reduce losses experienced by users.
On Monday, the development team behind NEAR Intents announced that they had successfully blocked over $50 million worth of assets connected to the breach and managed to freeze approximately $500,000. Chen further verified that Tether and Circle, both stablecoin issuers, placed a wallet associated with the exploit on their blacklists, resulting in the freezing of $318,013 in USDt (USDT) and USDC (USDC).
This security incident ranks among the largest attacks affecting the cryptocurrency sector in 2026, coming after a $320 million exploitation of the Liquid Network that occurred in September. Some of the most severe attacks in history include Bybit's breach in 2025, the 2022 Ronin Bridge incident that resulted in $615 million in losses, and the 2021 Poly Network compromise that saw $611 million stolen.
When Bitget first disclosed the incident, the exchange reported having halted withdrawals after losing $352 million worth of digital assets during Thursday's attack. Subsequently, Chen revised the incident report to account for a "more complete accounting of transfers," revealing that approximately $388 million had been compromised.
Who's responsible for the attack?
During her conversation with Cointelegraph, Chen also discussed the potential perpetrators behind the security breach. In the immediate aftermath of the attack, she suggested that North Korea might have been involved, citing "IP addresses that match the VPN choices by a certain [Democratic People's Republic of Korea] group," though she noted that Bitget had not "totally ruled out" the scenario of an inside job:
"This is a very complicated matter that we need to do a lot of investigation and quite thoroughly [sic] investigation. It's more based on our preliminary results of the investigation, we have ruled out that possibility."
The exchange has started to restore withdrawal functionality for its users in a phased approach, beginning with Bitcoin (BTC) transactions on Monday and moving forward with ETH on Tuesday.