Bitcoin Node Operators Urged to Update as Core Lightning Reports Active Attacks
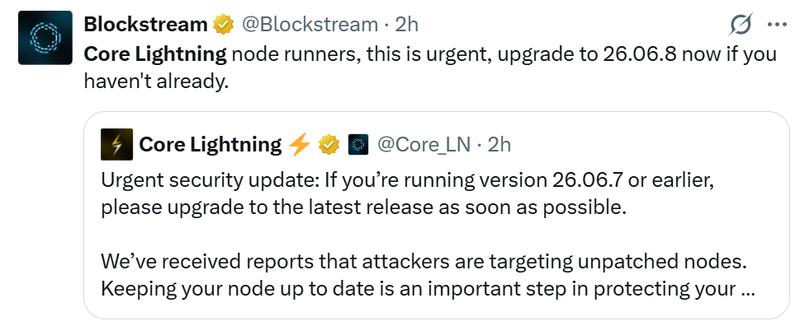
In response to reports of active exploitation attempts, Core Lightning has issued an urgent advisory for users operating version 26.06.7 or older to immediately update their software.
Developers responsible for Core Lightning, which provides open-source node software for the Bitcoin Lightning Network, have issued an urgent warning to users running outdated versions, instructing them to perform immediate upgrades following intelligence about attackers actively exploiting unpatched systems.
"Urgent security update: If you're running version 26.06.7 or earlier, please upgrade to the latest release as soon as possible," the team said on Friday.
The announcement from Core Lightning stopped short of identifying the specific vulnerabilities being exploited by threat actors or detailing the scope of potential damage. Cointelegraph reached out to Core Lightning for comment.
Earlier on Sept. 16, Core Lightning disclosed it was examining intelligence regarding a possible security concern related to experimental functionalities in Core Lightning that had the potential to affect user funds. Approximately six days following this disclosure, the development team pushed out version 26.06.8.
The Sept. 22 update delivered bug fixes alongside patches for "vulnerabilities responsibly reported by a number of sources." The release notes credit the Bitcoin Red Team and 12 other named individuals and groups, along with anonymous reporters.
Some of the fixes addressed flaws that could crash senders' nodes, requests that could exhaust memory in its REST interface and a channel-closing bug that could cause users to lose funds to a penalty, according to the changelog.
The development team made a strategic decision to deliberately exclude certain tests from the release, making it more difficult for malicious actors to perform reverse-engineering and weaponize the vulnerabilities during the window when operators were implementing the upgrades.
During August, Core Lightning disclosed it was developing a coordinated fix following its evaluation of an unusually high quantity of AI-generated Common Vulnerabilities and Exposures (CVE) reports submitted throughout the preceding weeks.
Two days later, it released 26.06.7 to address the confirmed vulnerabilities.