Across Protocol Issues Urgent Alert to Users Following Wallet Drainage Incidents
The Across Protocol team has issued an urgent advisory urging users to refrain from using its application while the team examines a potential domain security breach following multiple reports of drained wallets and missing funds.
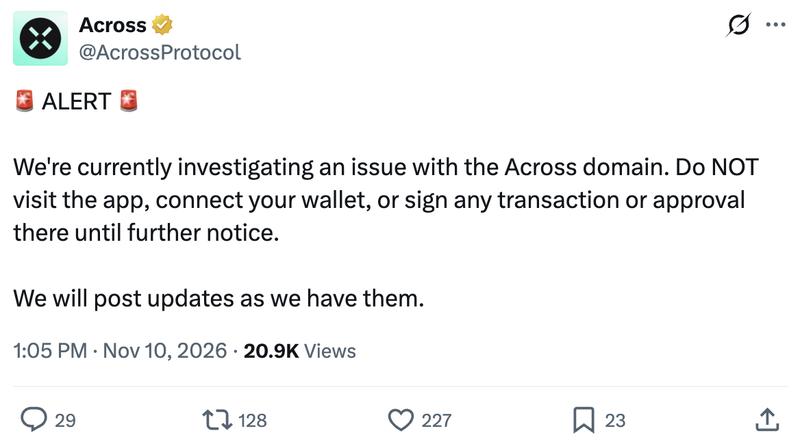
The crosschain bridging platform Across, which enables users to move digital assets between Ethereum and various other blockchain networks, issued an urgent warning on Tuesday advising users to stay away from its application and refrain from connecting their wallets as the team looks into a possible security breach.
Through a post published on X on Tuesday, Across cautioned users to avoid signing any transactions or approvals until additional information becomes available, while refraining from providing specific details about the incident's nature or confirming whether the website itself had fallen victim to a compromise.
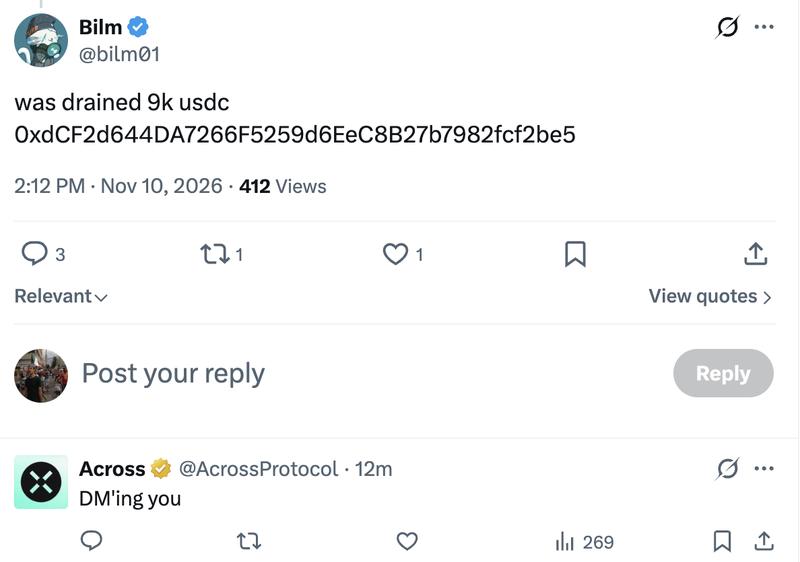
Multiple users took to X to share their experiences, with one individual claiming they had suffered a loss of $9,000 in USDC, while a separate user reported the disappearance of 7,053 USDT0 spanning seven separate transactions on the Plasma blockchain.
An additional user reported that their wallet had been completely drained following multiple uses of the bridge, claiming that the website itself had been subject to a compromise. The Across team responded by requesting transaction details from these users to further investigate their claims.
These reports have not been independently confirmed by Cointelegraph. When contacted for additional information, Across Protocol had not provided an immediate response to Cointelegraph's inquiry.
NEAR AI discloses separate security breach
In an unrelated security incident, NEAR AI made a disclosure on Monday revealing that malicious actors had successfully exploited a vulnerability within its artificial intelligence infrastructure, resulting in the exposure of account information belonging to roughly 100 users alongside data from 18 AI agents.
Based on an incident report dated Nov. 9, the attackers leveraged a remote code execution vulnerability present in SGLang, which is an open-source artificial intelligence inference engine, enabling them to gain unauthorized access to an internal server as well as additional infrastructure components. The data that was compromised encompassed user names, email addresses, chat histories from agents, settings and logs, with two customers having their API keys exposed as well.
NEAR AI indicated that the attackers may have also been able to observe requests that were processed on the server that had been compromised, which included those running under confidential mode. The organization stated that it had successfully patched the vulnerability, revoked all exposed credentials and restored access to its cloud services infrastructure.